Shared Hosting
 WordPress Hosting
 Cloud VPS Hosting
 Dedicated Servers
Hosting Outside the US Starts With the Provider, Not the Server
Last reviewed: September 2026
An American who decides to move their site offshore usually does the same thing: they open their existing cloud provider's console, change the region from Virginia to Frankfurt or Ireland, and consider the job done. The data is now physically in Europe. The legal position has barely moved.
This is the thing to understand first about hosting outside the US. The important question is not where the disk sits, but which provider controls the data and which courts can exercise jurisdiction over that provider. A provider subject to US jurisdiction can be required under the Stored Communications Act, as amended at 18 U.S.C. §2713, to produce data in its possession, custody or control even when that data is stored outside the United States.
The short version: moving to an independent non-US provider changes the legal route to your data and the rules your host operates under. Changing region at a US-jurisdiction provider does not. Neither one puts you personally outside US law, neither reliably helps with state regulation of your website, and hosting abroad brings your material within the reach of a second country's law as well. That last point is real and offshore hosting pages rarely explain it.
| Setup | What changes legally |
|---|---|
| US provider, US region | Provider and data are directly inside the US legal framework. |
| US provider, European region | The data location changes, but the provider can still be subject to US disclosure obligations. |
| Independent Finnish provider | The host operates under Finnish and EU law, and ordinary US compulsory process is no longer the same direct route. |
| Independent Swiss provider | The host operates under Swiss law and Swiss international-assistance procedures. |
Does the CLOUD Act apply to servers outside the US?
Yes, where the provider is subject to US jurisdiction. The Clarifying Lawful Overseas Use of Data Act, passed in 2018, amended the Stored Communications Act to settle what had been fought over in court for years. The provision it added says a provider must comply with obligations to preserve, backup or disclose communications and records within its possession, custody or control, regardless of whether that material is located within or outside the United States.
The test turns on jurisdiction over the provider. US authorities must have personal jurisdiction over the company to compel production, and once they do, the location of the server is not by itself a defence. Moving a US-jurisdiction provider's data from Virginia to Frankfurt does not remove that provider's US disclosure obligations. Eurojust's analysis of the CLOUD Act and the Cross-Border Data Forum's FAQ on its scope both set out the mechanics in detail.
European storage is not pointless. It can matter for GDPR, local regulation, contractual commitments and conflict-of-law questions. What it does not do is change who can be compelled.
Region selection is not jurisdiction selection. Every major American cloud provider offers European regions, and none of them removes the provider from US jurisdiction. When AWS launched its European Sovereign Cloud in Brandenburg in January 2026, it emphasised EU data residency, separate European legal entities, EU-based operational control and independent governance. Its public materials do not describe the service as categorically immune from US legal process.
The conflict with European law is unresolved. The CLOUD Act also allows the US to sign executive agreements giving foreign governments reciprocal access. As of 2026 only two are in effect, with the United Kingdom and Australia, and EU negotiations continue. Article 48 of the GDPR means a third-country judgment or administrative decision may only be recognised or enforced on the basis of an international agreement such as a mutual legal assistance treaty, which creates genuine conflict-of-law questions when a US order reaches data protected by European law. The European Data Protection Board set out its reading in Guidelines 02/2024.
None of this is unique to the United States. In 2024 the Royal Canadian Mounted Police served a production order on OVHcloud's Canadian subsidiary for account data held on servers in France, the UK and Australia, going around the mutual legal assistance treaty with France. An Ontario court declined to revoke it in September 2025 and the company has continued to contest it. The pattern is the same everywhere: a state reaching data abroad through a local corporate presence. The CLOUD Act is simply the largest version, because so much of the market is American.
What else is driving the question
Section 702 lapsed, and nothing changed
On 12 June 2026, Section 702 of the Foreign Intelligence Surveillance Act expired for the first time since 2008, after Congress failed to agree on reauthorization. Collection continued anyway. The FISA Court had approved the current certifications in March 2026, and those remain operational until March 2027 regardless of whether the underlying statute is in force, as EPIC noted at the time. Reauthorization was still unresolved in September 2026. The Congressional Research Service overview covers the statute and the 2024 amendments, and the Brennan Center maintains a running resource page. If you want one illustration of how far the practical position can diverge from the headline, this is it.
National security letters can carry gag orders
Under 18 U.S.C. §2709 the FBI can demand specified subscriber and transactional records without first obtaining a court order. A nondisclosure requirement can also be imposed where an authorised official certifies that disclosure could create one of the harms listed in the statute, such as interfering with an investigation or endangering national security. Recipients have a statutory right to seek judicial review of both the request and the gag.
There is still no comprehensive federal consumer privacy law
The United States has federal privacy statutes, but they are sector-specific, covering health records, children's data, credit reporting and similar. There is no omnibus federal consumer privacy regime. What exists instead is a growing patchwork of state laws with differing definitions, thresholds and enforcement.
State regulation of websites is expanding fast
After the Supreme Court upheld Texas HB 1181 in Free Speech Coalition v. Paxton in June 2025, applying intermediate rather than strict scrutiny, age-verification requirements spread quickly. The Congressional Research Service summary explains what the Court decided and why the standard it applied matters. By mid-2026, 27 states had adult-content age-verification laws in effect, with further categories covering social media and app stores under active legislation and litigation.
What changes when you use a non-US provider
The ordinary US compulsory route changes. A warrant served on a provider subject to US jurisdiction is a very different proposition from seeking data held by an independent Finnish or Swiss provider with no US presence. In the second case, compulsory access will generally require an international cooperation mechanism and compliance with the law applicable in the provider's own jurisdiction, rather than treating the foreign host as a domestic US provider.
Your host answers to a different set of rules. Retention duties, disclosure duties and the tests an order must meet come from the provider's own jurisdiction. Ours are set out in detail in our guides to Finnish hosting law and Swiss data protection law.
You may have a better chance of being notified. A provider outside US jurisdiction is not bound by a US gag order merely because the requesting authority would prefer secrecy. But its own country's law may restrict notification in some circumstances. The honest promise any provider can make is notification when legally permitted, not guaranteed notification, and you should treat a guarantee as a warning sign.
Your provider operates under a comprehensive data protection framework. Finland is subject to the GDPR and Switzerland to the Federal Act on Data Protection. The United States relies instead on a mixture of federal sector-specific rules and state privacy statutes rather than one general regime.
Does hosting outside the US change how DMCA notices work?
It can, and this is where the abstraction becomes concrete. Here is how it works on our own network, documented in our acceptable use policy, because the split is unusually clear-cut.
Our Finland footprint runs across two upstream networks with different obligations. On AS207003, our direct-to-datacenter connection, services operate under EU and Finnish law only. A US DMCA notice is not actioned there without a Finnish court order or an equivalent instrument recognised under Finnish law. Content complaints follow a standard notice-and-counter-statement process, and we remain bound by EU Digital Services Act obligations to remove genuinely illegal content on lawful notice.
On AS24940, a Tier-1 upstream lease, the position is different. That provider forwards DMCA notices with a compliance deadline, typically 24 hours, and we are contractually required to act within it to preserve network availability for everyone else on that segment. No counter-statement is available there, and expedited live-event takedowns apply on that network only.
Two networks, one country, one company, materially different exposure to a US legal instrument. That is what jurisdiction looks like at the operational level, and it is why the question is always which specific provider and which specific network, not which flag is on the data centre.
What you trade, which offshore hosting pages rarely explain
Moving your hosting abroad does not make you lose the First Amendment. It still limits what the US government can do to you. What changes is that your host and, depending on the circumstances, the material it hosts can also be subject to the laws of the hosting jurisdiction. Finland and Switzerland both protect freedom of expression, but neither reproduces the unusually broad US framework, and both prohibit some categories of expression that US law may protect.
So the two concerns people bring to this decision need separating. If your concern is direct compulsory access through a US-jurisdiction provider, changing to an independent non-US provider can materially change the legal route to the data. If your concern is controversial but lawful speech, foreign hosting introduces a different question: whether that speech is lawful in the country where the provider operates. Those are separate threat models and the same move does not necessarily solve both.
Three further things that do not change:
- US law still applies to you. If you live in the United States, US courts, US subpoenas and US law enforcement have jurisdiction over you, your devices and your accounts. Moving the server protects the server. It does not relocate the person.
- State website regulation can follow your users. Many state online-safety laws are triggered by providing covered services to residents of that state, not by where the server sits, though the exact test varies by statute. Texas has also shown willingness to reach foreign operators, obtaining a writ against Verisign in 2026 over a domain run by a Luxembourg company after a default judgment.
- Your own compliance duties stay put. A US business remains responsible for its obligations to its customers regardless of where the data sits.
The .com problem
You can move your servers to Zurich and still hold an important part of your setup inside American jurisdiction, because Verisign, which operates the entire .com and .net zone, is a Virginia company. A domain can be placed on hold at the registry regardless of where the website behind it is hosted, and 2026 produced a clear demonstration of how far that reaches.
If jurisdiction is the reason you are moving, the domain deserves the same thought as the server. We covered the whole picture, including which extensions answer where, in who can actually take your domain away and which registries redact your data.
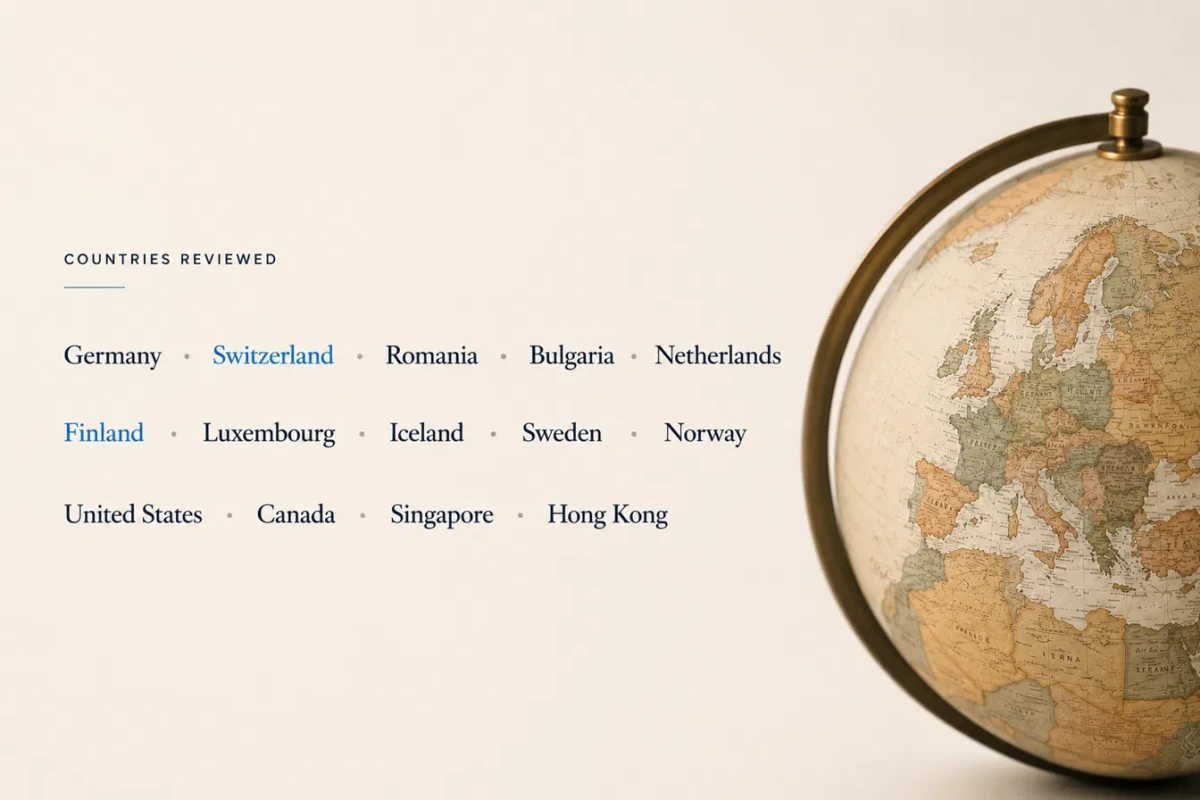
Switzerland or Finland, for an American
SWITZERLAND OUTSIDE THE EU
Outside both the US and the EU, applying its own Federal Act on Data Protection and its own international assistance procedures rather than either country's framework. It costs more than Finland across our range.
FINLAND BETTER VALUE
GDPR protection, strong constitutional protection for confidential communications, a consistently high placing in press-freedom rankings, and lower prices. The trade-off is that EU membership means production orders from other EU states move faster under the EU e-Evidence Regulation, which has applied since August 2026. That system governs cross-border orders within the EU and does not cover US requests.
Worth being blunt about latency, since this is the one place American buyers are genuinely worse off than European ones. A server in Helsinki or Zurich is meaningfully further from your US visitors than one in Virginia. For many ordinary websites, the additional latency is measured in tens of milliseconds and is often much less noticeable than page weight, caching and application performance. For a latency-sensitive application it is real, and you should measure rather than assume. Our looking glass lets you test the route from your own connection before buying anything. The full country comparison is in Finland versus Switzerland.
For American customers at Packetra
We are not a US company. No US entity, no US staff, no US infrastructure. That is the distinction this whole article turns on, and it is the one thing a region dropdown cannot give you.
Signup takes an email address, with no identity check, no document upload and no phone verification. Prices can be shown and paid in US dollars, and we accept Bitcoin and Monero through a BTCPay Server we run ourselves, so crypto payments do not pass through a third-party processor that can apply its own verification.
One thing to be straightforward about, since the age-verification wave is pushing some adult-site operators to look abroad. Adult-content policy depends on location and network. In Finland, lawful adult content is permitted on our AS207003 network and must be arranged with support before ordering; it is not permitted on our AS24940 segment. Lawful adult content is permitted in Switzerland. None of that changes an operator's obligations under US state age-verification laws where those laws apply. Tor exit nodes are not permitted at either location, and peer-to-peer traffic is not permitted in Finland.
Shared and WordPress hosting carry a 30 day money-back guarantee. If you are moving an existing site, our migration guide covers doing it without downtime.
Research note. This article was prepared using primary legislation, court decisions, regulator material and Packetra's first-hand experience handling hosting and abuse requests across its Finland and Switzerland infrastructure. Legal and regulatory information was last checked in September 2026. Several facts here are time-sensitive, particularly the Section 702 position and the EU e-Evidence Regulation. This is general information, not legal advice for your situation.
Frequently asked questions
Does hosting my data in a European region of a US cloud provider protect it?
Not from US legal process. A provider subject to US jurisdiction can be required to produce data in its possession, custody or control regardless of where it is stored. European storage can still matter for other purposes, including European data protection obligations, but it does not change who can be compelled.
Can US authorities get my data from a foreign host?
Where the provider has no US presence, not through ordinary US compulsory process. Access would generally require an international cooperation mechanism and compliance with the law of the provider's jurisdiction. That is slower and more constrained, but it is a real route, not a theoretical one.
Is it legal for an American to host their website abroad?
Yes. There is no restriction on where a US person or business hosts a website, and many American companies host abroad for cost, latency or compliance reasons.
Did Section 702 expiring change anything?
Not in practice. The statute lapsed in June 2026, but the FISA Court had already approved certifications running to March 2027, and those remain operational. The lesson is that the legal headline and the operational reality can diverge for a long time.
Will hosting abroad protect me from state age-verification laws?
Generally no. Those laws are typically triggered by serving residents of the state rather than by server location, though the test varies by statute. A state can also pursue foreign operators, as Texas has demonstrated.
Do I lose free speech protection by hosting in Europe?
You do not lose the First Amendment, which still constrains the US government. What you add is a second body of law: your host, and potentially the material it hosts, comes within the reach of the hosting country's rules, and neither Finland nor Switzerland protects expression as broadly as US law does in every category.