Shared Hosting
 WordPress Hosting
 VPS Hosting
 Dedicated Servers
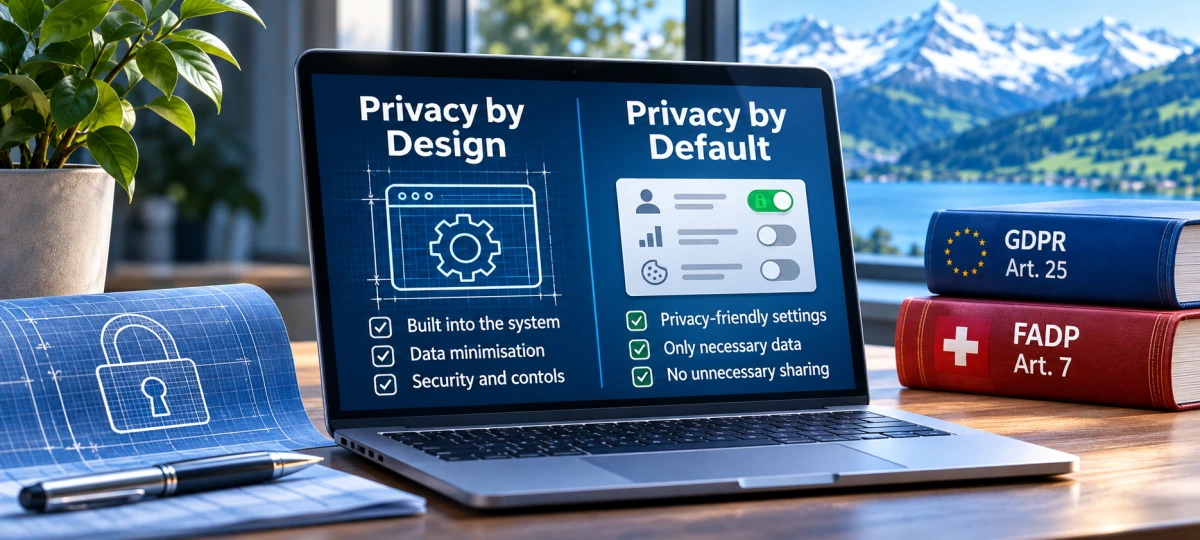
Privacy by design vs privacy by default trips people up because the two sound like one idea. They are two halves of one legal duty, set out in Article 25 of the GDPR and Article 7 of Switzerland's Federal Act on Data Protection (FADP). They answer different questions. Privacy by design is about how a system is built. Privacy by default is about how it behaves before anyone changes a setting. This guide explains both, where EU and Swiss law differ, and what the pair means when you choose where to host a website.
The short version
Privacy by design means building data protection into a system from the planning stage. Privacy by default means the settings a person gets without doing anything collect and expose only what the purpose needs. A system can pass the first test and fail the second: a private-account option is good design, but making every new account public by default is a default failure. Both bind whoever decides how personal data is processed, and that includes your choice of hosting.
Privacy by design vs privacy by default at a glance
| Privacy by design | Privacy by default | |
|---|---|---|
| The question it answers | Is data protection built into the system? | What happens if the user changes nothing? |
| When it applies | From planning, and throughout processing | Every time someone starts using the system |
| Typical measures | Data minimisation, pseudonymisation, encryption, access control, deletion schedules | Opt-in rather than opt-out, private profiles, non-essential tracking off, short retention |
| GDPR | Article 25(1) | Article 25(2) |
| FADP | Article 7(1) and 7(2) | Article 7(3) |
Privacy by design: how the system is built
The idea goes back to Ann Cavoukian, Information and Privacy Commissioner of Ontario from 1997 to 2014, who argued that privacy should be engineered into systems rather than bolted on afterwards. The GDPR turned it into law. Article 25(1) requires the controller, the organisation that decides how and why personal data is processed, to put appropriate technical and organisational measures in place, both when deciding how processing will work and while it runs. The article names pseudonymisation and data minimisation as examples, and lets the controller weigh the state of the art, the cost, the nature and purpose of the processing, and the risk to people.
Switzerland's version is close. FADP Article 7 obliges the controller to arrange processing in technical and organisational terms so that it meets data protection rules, in particular the principles in Article 6, from the planning stage onwards. The measures must suit the state of the art, the type and scope of processing, and the risk to the people concerned.
For a website, privacy by design looks like this: forms that ask only for the fields you use, encrypted connections and storage, access limited to the people who need it, logs that do not keep more than they must, and data deleted on a schedule rather than kept forever.
Privacy by default: what happens before anyone changes a setting
Article 25(2) of the GDPR requires that, by default, only the personal data necessary for each specific purpose is processed. That covers four things: the amount of data collected, how far it is processed, how long it is stored, and who can access it. By default, personal data must not be made accessible to an indefinite number of people without the person's own intervention.
FADP Article 7(3) says the same in fewer words: the controller must use suitable default settings to limit processing to the minimum the purpose requires, unless the person concerned chooses otherwise.
This rule does not forbid all further processing. It means the starting settings stay at the minimum, and anything beyond that still needs a valid legal basis; where that basis is consent, the person has to actively give it. Newsletter boxes start unticked, analytics that need consent stay off until consent is given, profiles start private, and data that is not needed is not collected just because the form could ask.
CaseWhen the default is the problem
On 1 September 2023, Ireland's Data Protection Commission fined TikTok EUR 345 million over its processing of children's data. One finding was that child accounts were set to public by default, which the regulator held contrary to data protection by design and by default under Articles 25(1) and 25(2). The option to go private existed. The default was the failure.
GDPR and FADP side by side
| GDPR (EU) | FADP (Switzerland) | |
|---|---|---|
| Provision | Article 25 | Article 7, in force since 1 September 2023 |
| Who is bound | The controller | The controller |
| Enforcement | Administrative fines on the organisation of up to EUR 10 million or 2% of worldwide annual turnover | Article 7 is not itself a criminal offence. The supervisory authority can order changes, and wilful breaches of related duties, such as using a processor without meeting Article 9, carry fines of up to CHF 250,000 on the individuals responsible |
Our guide to Swiss data protection law covers the FADP in more depth.
What privacy by default means for your hosting
Your hosting provider usually acts as a processor for the personal data on your website, handling it on your behalf, while acting as a separate controller for its own customer and billing records. The GDPR requires controllers to use only processors that give sufficient guarantees of appropriate measures, and the FADP requires the controller to make sure a processor can guarantee data security. Choosing a host is part of your own privacy by design, and its defaults become your defaults.
1. What the host collects about you. Some hosts ask for your full name, postal address, phone number or an ID document at signup. Ask which details are required and why; a host that offers email-only registration keeps the personal data tied to your account to a minimum. Our guide to no-KYC hosting explains the difference.
2. What the host can see and keep. Ask what it logs, for how long, and who can access your server. Our guide to what your hosting provider can see goes through it.
3. Where data and backups are stored. The location affects which authorities can reach your data and which legal procedures apply, and so do the host's own jurisdiction and legal obligations. Finland vs Switzerland compares our two locations.
4. What your site loads by default. Themes and plugins often pull fonts, analytics and embeds from third parties on every page view, before any consent. A fresh WordPress install, for instance, shows Gravatar avatars by default, so pages with comments make visitors' browsers contact an outside service. Our guides to Google Fonts and GDPR and running WordPress without Google show how to switch those calls off.
5. The contract. Ask for a data processing agreement that says what the host may do with your data and nothing more.
On our side, signup takes an email address and a password, with no ID, phone number or postal address, and Bitcoin and Monero payments go through our own BTCPay Server rather than a third-party processor. Our privacy policy sets out what we keep and when we hand anything over.
FAQ
Is privacy by design the same as privacy by default?
No. Privacy by design is about building protection into the system. Its counterpart is about the settings people get when they do nothing. The law requires both, and a system can meet one while failing the other.
Is privacy by default mandatory?
Yes, for controllers under the GDPR and the FADP. Both laws require default settings that limit processing to what the purpose needs.
Do protective default settings mean I need consent for everything?
No. It means the minimum is the starting point. People can choose to share more, and processing that is necessary for the service can run without extra opt-ins.
Does it apply to small websites?
Yes. Neither law exempts small controllers from these duties, though what counts as appropriate scales with the risk. A contact form needs fewer measures than a health app, but it still should not collect more than it uses.
Does my hosting provider have to follow Article 25?
Article 25 binds the controller, which is usually you. Your host is bound by its processor contract and by its own security duties, and you are responsible for choosing a host that can meet them.
Sources
- Regulation (EU) 2016/679 (GDPR), EUR-Lex: Articles 25, 28 and 83
- FADP Article 7: Data protection by design and by default
- FADP Article 61: Violation of duties of diligence
- Data Protection Commission (Ireland): Data protection by design and by default
- McCann FitzGerald: DPC fines TikTok EUR 345 million (decision of 1 September 2023)
- European Data Protection Board, Guidelines 4/2019 on Article 25 Data Protection by Design and by Default, version 2.0
- Swiss Confederation, SME Portal: New Federal Act on Data Protection (nFADP)
Last reviewed: 11 November 2026
Research note: Legal provisions are summarised from the GDPR and FADP texts in force at the review date. This article is general information about data protection law, not legal advice; if your processing carries real risk, take advice from a data protection specialist in your jurisdiction.